CloudLinux Resource Isolation: 5 Practical Ways It Protects Shared Hosting
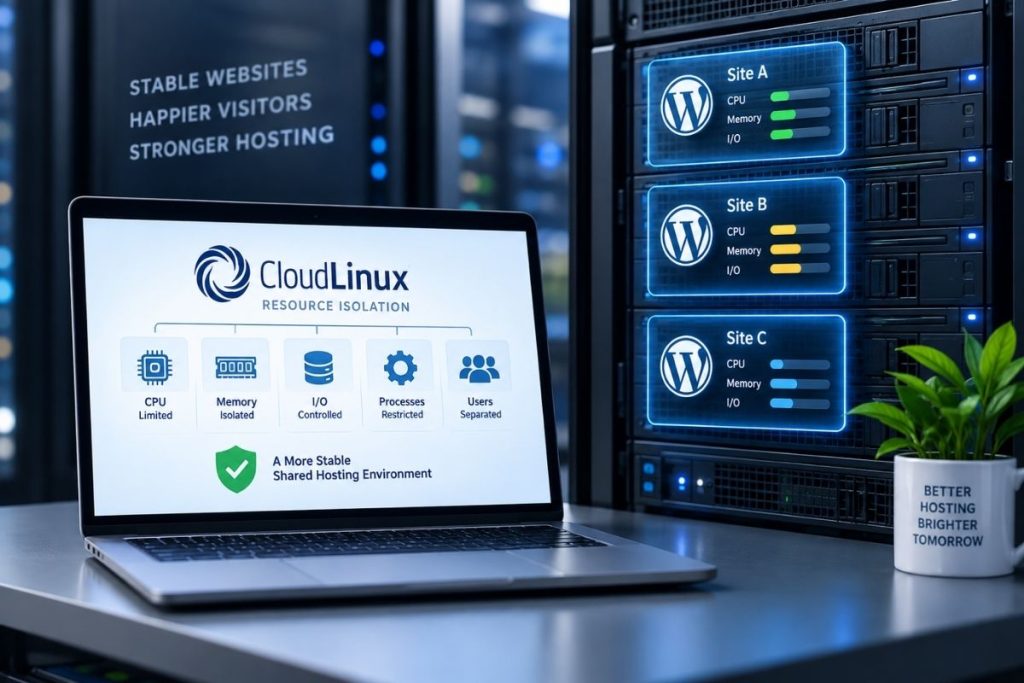
CloudLinux Resource Isolation is designed to solve one of the most frustrating problems in shared hosting: one account consuming enough resources to affect websites that have nothing to do with the workload.
This is usually called the “noisy neighbor” problem.
Imagine one WordPress site starts a large backup while another runs an import and a third receives a burst of bot traffic. All three are using the same physical server. Without sensible account-level controls, one demanding workload can compete aggressively for CPU, memory, disk access or web-server processes.
CloudLinux addresses this by placing hosting accounts inside Lightweight Virtual Environments, or LVEs, and controlling how much of those resources each account can consume.
The result is not unlimited performance. It is controlled sharing: one busy account may slow down or hit its own limit, but it is less likely to drag unrelated websites down with it.
CloudLinux Resource Isolation Starts with LVE
LVE is a kernel-level resource-control system used by CloudLinux OS. It can place limits on CPU speed, physical memory, disk I/O, IOPS, process count and entry processes for individual hosting accounts.
CloudLinux’s own documentation gives a useful sense of the scale involved. A documented “typical hosting account” example uses:
- CPU speed: 100% of one core
- Physical memory: 1 GB
- Disk I/O: 1024 KB/s
- IOPS: 1024 operations per second
- Processes: 100
- Entry processes: 20
CloudLinux also shows a higher-end example with 200% CPU, 2 GB of memory and 4096 KB/s of I/O. These are documented example configurations, not universal values that every hosting provider should copy.
The important point is that the limits can be set per account or package. A provider can therefore give different hosting plans different resource ceilings rather than treating every customer identically.
The official CloudLinux limits documentation explains the available limits and how they behave.
What Actually Happens When a Limit Is Reached?
This is where resource isolation becomes more practical than a simple list of specifications.
CloudLinux documents different behaviour depending on which resource is exhausted.
If an account reaches its CPU or I/O limit, the website normally becomes slower because work is being throttled rather than allowed to consume more of the server.
If physical memory or process limits are exhausted, PHP or CGI requests can fail and the visitor may see 500 or 503 errors.
Entry processes behave differently again. When the EP limit is reached under Apache, CloudLinux can return a 508 Resource Limit Reached response rather than allowing the account to consume all available Apache processes.
That distinction is useful when troubleshooting. “The site is slow” and “the site is returning 508 errors” can point to very different resource problems.
A 508 Error Is Not Automatically a Server Failure
Suppose a WooCommerce site begins returning occasional 508 errors during a promotion.
The first reaction might be to assume the server is overloaded. But a 508 on a CloudLinux environment can mean the account itself has reached its entry-process limit while the rest of the server is still operating normally.
That is exactly what isolation is intended to do: contain the pressure.
The next step should be diagnosis rather than immediately raising every limit. Useful questions include:
- Are PHP requests taking too long to complete?
- Is a plugin generating slow database queries?
- Is bot traffic creating too many concurrent requests?
- Did a scheduled task or backup overlap with peak traffic?
- Has the site genuinely outgrown the resources assigned to its plan?
CloudLinux Manager and tools such as lvetop can help administrators review current resource usage rather than guessing from the symptom alone.
CPU and I/O Limits Solve Different Problems
CPU limits are most relevant when code is doing expensive computation. A badly configured backup plugin, image-processing job, import task or inefficient PHP workload can consume a large amount of processor time.
Disk I/O limits address a different bottleneck.
A site performing large backups, imports or heavy file operations may not use unusual amounts of CPU but can still put pressure on storage. On a busy shared server, aggressive disk activity from one account can affect database and file access for others.
CloudLinux limits those two resource types separately because a site can be CPU-heavy, I/O-heavy or both.
For a broader explanation of how these resources affect hosting performance, see our guide to cPanel Performance Hosting.
Memory Limits Can Expose Problems That Need Fixing
Physical memory limits prevent one account from consuming an unlimited amount of RAM.
If a PHP process, plugin or application repeatedly exhausts the account’s memory allocation, the result may be failed requests rather than the entire server running out of memory.
That is protective for other customers, but it is not a fix for the affected website.
Repeated memory faults can indicate inefficient code, a large workload, too many PHP workers or a hosting plan that no longer matches the application.
Simply increasing memory without investigating the cause may hide the symptom while leaving the underlying problem unchanged.
CageFS Solves a Different Shared-Hosting Problem
LVE deals mainly with resource usage. CageFS deals with filesystem isolation.
CloudLinux describes CageFS as a per-user virtualized filesystem that places each customer inside a separate “cage.” The purpose is to stop hosting users from seeing each other’s files or sensitive system information they do not need.
This separation is important on a server hosting many unrelated customers.
However, CageFS should not be confused with application security. If a WordPress plugin has a vulnerability, CageFS does not repair that plugin. Its role is containment: reducing the ability of one compromised hosting account to expose unrelated customer data.
The official CloudLinux Manager documentation describes CageFS and its account-level controls.
The Limits Themselves Need Sensible Configuration
CloudLinux does not automatically make every shared-hosting plan well designed.
If limits are set too low, normal websites can be throttled unnecessarily. If they are set too high, a demanding account may receive so much headroom that the protection becomes less meaningful.
CloudLinux even recommends that CPU speed limits should generally not be set below 100%, because very low CPU limits can increase context-switching overhead.
That is an important operational point: resource isolation still requires judgement from the hosting provider.
The server also needs adequate hardware, monitoring, security, updates and sensible package design. CloudLinux adds control; it does not replace server management.
When Raising the Limit Is the Wrong Answer
If a website hits its resource limits occasionally during a short traffic spike, increasing the plan may be reasonable.
If it hits the same limit every day, the better question is why.
A provider might discover that a backup runs during business hours, a crawler is hammering uncached pages, a plugin creates expensive database queries or PHP workers are remaining busy for too long.
In those cases, optimization can be more valuable than simply allocating more resources.
On the other hand, a site with legitimate sustained demand may genuinely have outgrown shared hosting. At that point, continually increasing account limits can become less sensible than moving to a larger environment. Our guide to premium hosting for high-performance websites looks at that decision in more detail.
Does Resource Isolation Make Shared Hosting More Reliable?
Yes, within realistic limits.
CloudLinux cannot make shared hosting behave like a dedicated server because customers are still using common physical infrastructure.
What it can do is create enforceable boundaries around that shared infrastructure.
If one account becomes CPU-heavy, memory-hungry or overloaded with concurrent requests, the effect can be contained within that account instead of automatically spreading to every website on the machine.
For hosting providers, that makes capacity easier to control. For customers, it reduces the chance that another user’s poorly behaved workload becomes their performance problem.
The real value of CloudLinux Resource Isolation is not “more resources.” It is knowing where one customer’s resources end and another customer’s begin.
Reliable Hosting for a Seamless Online Experience
24/7 Support & High Performance – Host with Confidence
Boost Your Online Presence with Host Home: Unmatched Hosting Power, Anytime, Anywhere.
Contact us
© 2026 hosthome.cloud. All Rights Reserved.